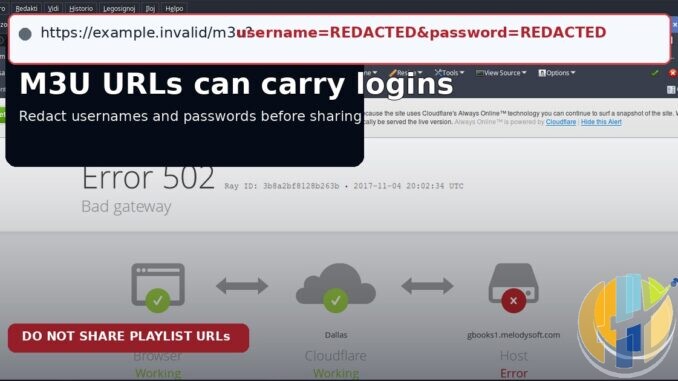
If your “playlist” looks like a long web address with your username and password sitting in the query string, congratulations: you have been carrying the keys in the window. Anyone who logs that URL, screenshots it, syncs it to a breached player backend, or forwards it in a family WhatsApp has your login. That is not clever IPTV. That is credential spray waiting to happen.
This piece is security hygiene for UK households. It explains why M3U-style links that embed logins are a leak by design, points at public warning patterns around IBO-style backend breaches without linking stolen lists, and tells you what to do instead: official apps with modern sign-in, certified boxes, and never pasting passwords into random APKs. Background reading: is IPTV legal and choose legal IPTV.
How a login ends up inside a URL
Older playlist formats grew up in a world where “put the user and pass in the link” felt convenient for hobby setups. The pattern is simple to recognise even without a tutorial:
- A long
httporhttpsaddress. - Query parameters that clearly name a user, password, token, or line identity.
- The same string pasted into multiple apps, sticks, and phones.
URLs get recorded everywhere polite software keeps history: CDN logs, proxy logs, crash reports, analytics, clipboard managers, and support screenshots. Browser referrers can leak them. Shared family notes can leak them. A “helpful” Telegram admin asking you to paste the full line so they can “fix it” has just collected the secret in clear text.
Licensed consumer apps mostly moved on. OAuth, device codes, salted tokens, and store-mediated sign-in keep the long-lived secret off the address bar. Grey IPTV playlists often did not.
IBO-style breach news as a warning (not a shopping list)
Community threads and security write-ups have warned that some unofficial player backends were breached and that credentials tied to those ecosystems were being circulated. Treat that class of news as a fire alarm, not a treasure map. Do not hunt stolen lists. Do not download “checker” tools. Do not paste your old playlist into a site that promises to validate it.
The consumer takeaway is dull and correct:
- If an unofficial player stored your MAC, playlist, or panel login on a weak backend, assume exposure.
- If you reused that password anywhere that matters, change it.
- Uninstall the risky APK. Prefer apps from Google Play or other official storefronts.
Kaspersky and others have also documented fake Android IPTV apps that skip the TV fantasy and install banking malware. After a scare, “replacement APKs” from random mirrors are how a bad week becomes a worse one.
Never paste credentials into random APKs
Hard rules for the household:
- Do not sideload an IPTV player because a chat said it is “the safe one this month.”
- Do not paste M3U or portal strings that contain passwords into any app you cannot name, update, or uninstall cleanly.
- Do not email yourself the full playlist “for backup.” Email is not a vault.
- Do not let a stranger screen-share while the playlist field is visible.
- Turn unknown sources off when you are done installing legitimate software.
Players are software with network permission. Giving them a password-bearing URL is giving them the keys and a microphone on your traffic.
Prefer OAuth and official signed-in apps
Build the living room on patterns that do not print secrets in the address bar:
- BBC iPlayer, ITVX, Channel 4, 5, Freely where supported.
- Netflix, Disney+, Prime Video, NOW, Sky apps, and other licensed services via official stores.
- Sign-in with device codes, QR, or account pickers instead of pasting raw passwords into third-party players.
- Certified Google TV / Android TV hardware that still receives Play Protect and store updates.
Yes, you will pay for what you watch. You will also avoid the day a leaked M3U turns into someone else watching on your line, or worse, reusing your password on email.
- Assume the URL is burned. Stop using it.
- Change any reused passwords on email, banking, and other logins.
- Uninstall unofficial IPTV APKs. Clear their data if the OS allows.
- Review Google account activity and Play Protect findings on the stick or box.
- Move viewing to licensed apps. Do not “re-buy a fresh line” as damage control for a leak.
Skeptic note: a seller who insists the only way to watch is a link with your password in clear text is asking you to accept 1990s security for 2026 risk. Pragmatist note: official apps already solved this with signed-in sessions. Use them.
A VPN on public Wi-Fi can be privacy hygiene. It does not make a leaked playlist safe, and it does not legalise unlicensed channels. We will not teach playlist theft, credential stuffing, or WAF bypass.
Best IPTV boxes to buy this month from Amazon
Never paste playlist URLs that embed a login. Use official sign-in on a clean player shell instead. Illegal IPTV is illegal. No Fire OS hero.
Affiliate disclosure: amazon.co.uk links use our Associates tag (hushamcom-21). We may earn a commission at no extra cost to you. Prices move. Check Amazon today. UK tag hushamcom-21; US tag hushamcom-20.
- Google TV Streamer 4K · Amazon US – flagship Google TV player for Freely-capable setups, Play Store apps, and a proper remote.
- Xiaomi TV Stick 4K (2nd Gen) · Amazon US – budget HDMI stick for official Netflix, YouTube, and UK catch-up apps when you confirm stock and model.
- Strong LEAP-AIR (UK listing — no clean US match) – UK-market Google TV stick for licensed streaming without babysitting grey portals.
- Nokia Streaming Box 8010 (UK listing — no clean US match) – Android TV box with Ethernet option for households that want a wired licensed stack.
- MECOOL KM2 Plus Deluxe · Amazon US – certified-leaning Android TV box for Play Store apps; check current certification for the BBC apps you care about.
Keep passwords out of URLs. Keep TV inside official signed-in apps. Let the next breach headline be someone else’s problem.